Free Advanced Cyber Security Course

Advanced Cyber Security - Threats and Governance

star 4.53  Beginner level 2.25 learning hrs 72.2K+ Learners

Learn solutions for cyber-attacks with Advanced Cyber Security-Threats and Governance free course

Cyber Security Analyst Career Certificate (6 course series)

This course is part of a guided series.

Key Highlights

Get free course content

Master in-demand skills & tools

Test your skills with quizzes

About this course

The threats related to Cyber Security are growing in frequency and complexity. These Cyber Security threats are taking the information security industry on a toll. In the last few years, we have witnessed the most horrific cases of cybercrimes as cyber attackers are getting smarter day by day. As the threat of compromising the data is increasing, the need for Cyber Security professionals is also increasing. The goal of this course is to strengthen the knowledge of current enthusiasts in the field. You will be introduced to some types of Cyber Security threats, popular attacks, vulnerabilities, landscape, policy, frameworks, and certificates This free course on Cyber Security will provide you a certificate on the completion of the course.

Launch your career in Cyber Security with Great Learning’s Cyber Security Certificate program and learn from the world-class leaders in the domain. The program has collaborated with the Stanford Centre for Professional Development that provides a world-class standard of learning.  Explore our best online cybersecurity courses designed for fresh graduates and working professionals.

Stand out with an industry-recognized certificate

10,000+ certificates claimed, get yours today!

Get noticed by top recruiters

Share on professional channels

Globally recognised

Land your dream job

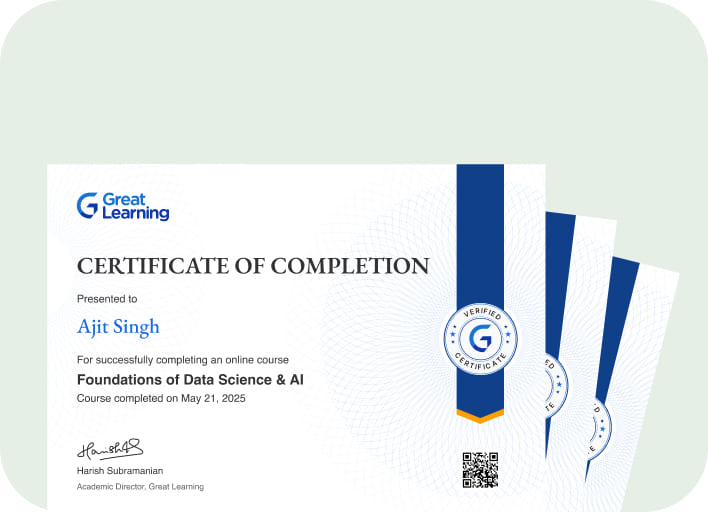
Certificate Image

Course outline

What are Threats?

This module will cover the actual definition of threats, their types, and causes. Next, you will learn about some potential threats to our systems and the people behind them.

GitHub DDos Attack

What are Vulnerabilities?

In this module, the tutor will brief you on the definition of vulnerabilities and their types. Later, you will learn about the term vulnerability analysis, which is used to analyze the potential weaknesses and loopholes in the system.

Vulnerability Categorization

SQL Injection Anatomy

Cross Site Scripting Anatomy

WordPress Plugin SQL Vulnerability

Kevin Mitnik's Website's XSS Vulnerability

Flickr XSRF Vulnerability

Password Security

Cyber Security Landscape

Cyber security Policy Management

Cyber Security Policy Ecosystem

Cyber Security Policy Management Design

Cyber Security FrameWorks

ISMS Environment

Frameworks and ISO27001 Standard

IS Policy Components

ISMS Certification - ISO 27001 Certification Process

Get access to the complete curriculum once you enroll in the course

Advanced Cyber Security - Threats and Governance

rating icon 4.53

2.25 Hours

Beginner

72.2K+ learners enrolled so far

Get free course content

Master in-demand skills & tools

Test your skills with quizzes

Showcase your complete skill set with a career certificate

Build skills with guided learning and prove your readiness for your future job role.

Cyber Security Analyst Career Certificate sample certificate

Cyber Security Analyst Career Certificate

6 courses series • Lifetime access

Know More

Level up with advanced skills & become job ready with Pro+

Subscribe to Pro+ today to build skills with 50+ Pro courses and prep for jobs with advanced AI tools.

PRO
Pro+ course thumbnail image
Risk and Threat Management Strategy
1 project 5 hrs video content

Practice exercises

Guided Projects

AI Resume Builder

AI mock interviews

Start 7-Day Free Trial

Trusted by 10 Million+ Learners globally

Learner reviews of the Free Courses

4.53
72%
20%
5%
1%
2%
Reviewer Profile

5.0

South Africa
“Advanced Cyber Security”
Cyber security is an interesting field. I wish one day to be part of cyber security data analysis and help people protect their data and personal information. Also, assist in mitigating cyber attack risks.
Reviewer Profile

5.0

India
“Advanced Cyber Security - Threats and Governance”
The Advanced Cyber Security - Threats and Governance certification course offers in-depth insights into modern cyber threats and robust governance strategies. It covers critical topics like threat detection, prevention, and incident response. Ideal for professionals, the course enhances skills to safeguard digital infrastructure and ensures compliance with security standards.
Reviewer Profile

5.0

India
“Advanced Cyber Security - Threats and Governance”
Threats and Governance focuses on identifying, mitigating, and managing cybersecurity threats while ensuring that governance policies and frameworks are in place to protect digital assets. It involves proactive defense mechanisms and strategic oversight to minimize risks and maintain security compliance.
Reviewer Profile

5.0

India
“The Advanced Cyber Security Course is Insightful, Covering Critical Threats and Governance Effectively”
The Advanced Cyber Security course on Threats and Governance from Great Learning is outstanding. It offers in-depth coverage of contemporary cyber threats and governance frameworks. The materials are well-organized, and the instructors provide valuable real-world insights. This course is essential for anyone looking to enhance their cybersecurity knowledge. Highly recommended!
Reviewer Profile

5.0

India
“It Was Good for Studying and Learning”
Cybersecurity is the practice of protecting systems, networks, and data from digital attacks, theft, damage, or unauthorized access. It encompasses a broad range of measures, technologies, and practices designed to safeguard information and maintain the integrity, confidentiality, and availability of data. Here are some key aspects: ### **1. Core Principles (CIA Triad):** - **Confidentiality:** Ensuring that information is only accessible to those authorized to view it. This is often achieved through encryption and access controls. - **Integrity:** Maintaining the accuracy and consistency of data over its lifecycle. This involves protecting data from being altered or corrupted by unauthorized individuals. - **Availability:** Ensuring that information and resources are accessible to authorized users when needed, which involves protecting against disruptions, such as denial-of-service attacks. ### **2. Key Areas of Cybersecurity:** - **Network Security:** Protecting the integrity, confidentiality, and accessibility of data as it is transmitted across or accessed through a network. - **Endpoint Security:** Securing individual devices like computers, smartphones, and tablets from threats. - **Application Security:** Ensuring that software and applications are secure from threats and vulnerabilities, often through code reviews, testing, and patch management. - **Data Security:** Implementing measures to protect data from unauthorized access and breaches, including data encryption and secure storage practices. - **Identity and Access Management (IAM):** Managing user identities and their access rights to ensure that only authorized individuals can access specific resources. - **Incident Response:** Preparing for and responding to security breaches or incidents to mitigate damage and recover quickly. - **Security Operations:** Continuous monitoring and management of security systems and practices to detect and respond to threats in real-time. ### **3. Common Cybersecurity Threats:** - **Malware:** Malicious software, including viruses, worms, trojans, and ransomware, designed to damage or gain unauthorized access to systems. - **Phishing:** Attempts to trick individuals into providing sensitive information, typically through deceptive emails or websites. - **Denial-of-Service (DoS) Attacks:** Overloading systems or networks to make them unavailable to users. - **Man-in-the-Middle (MitM) Attacks:** Intercepting and potentially altering communication between two parties without their knowledge. - **SQL Injection:** Exploiting vulnerabilities in web applications to execute malicious SQL commands. ### **4. Best Practices:** - **Regular Updates and Patching:** Keeping software and systems up-to-date to protect against known vulnerabilities. - **Strong Authentication:** Using multi-factor authentication (MFA) and strong passwords to enhance security. - **Security Awareness Training:** Educating employees and users about potential threats and safe practices. - **Regular Backups:** Ensuring that data is regularly backed up and can be restored in case of loss or corruption. ### **5. Regulatory Frameworks and Standards:** - **ISO/IEC 27001:** Provides a framework for establishing, implementing, maintaining, and improving an information security management system (ISMS). - **NIST Cybersecurity Framework:** Offers guidelines for managing and mitigating cybersecurity risks. - **GDPR:** A regulation in the European Union focused on data protection and privacy. Cybersecurity is an ever-evolving field as new threats and technologies emerge. Staying informed and proactive is essential for protecting information and maintaining security.
Reviewer Profile

5.0

India
“Threats and Governance in Cyber Security”
Very interesting and easy to learn. The most important thing is it is free of cost, so anyone can have a certificate in this course, which will help in improving their resume.
Reviewer Profile

4.0

India
“A Cyber Security Course is an Invaluable Opportunity to Recognize the Significance of Digital Safety in Our Daily Lives”
Ultimately, the course cultivates a culture of awareness and empowerment, equipping participants with the knowledge to recognize threats and implement effective protective measures. This appreciation not only enhances individual skills but also contributes to the overall resilience of organizations in the face of cyber challenges.
Reviewer Profile

5.0

South Africa
“My Highlight Was Learning Advanced Cyber Security”
Comprehensive Security Framework: Provides a detailed set of guidelines and best practices covering various dimensions of information security.
Reviewer Profile

4.0

India
“Good Course for Beginners Who Want to Study Information Security”
Good course for beginners who want to study information security. Best for college graduates. Very informative course and very well explained. I gained a lot of knowledge and my concepts are clear now.
Reviewer Profile

4.0

India
“Very Good Course to Help in Understanding the Advanced Cyber Security”
Very good course to help in understanding the Advanced Cyber Security.

Frequently Asked Questions

Will I receive a certificate upon completing this free course?

Yes, upon successful completion of the course and payment of the certificate fee, you will receive a completion certificate that you can add to your resume.

Is this course free?

Yes, you may enroll in the course and access the course content for free. However, if you wish to obtain a certificate upon completion, a non-refundable fee is applicable.

What is cyber governance?

Cyber governance refers to the system using which an organization assesses and manages cyber threats, determines security strategies, and makes informed decisions using available resources. Think of it as a sub-function of organizational governance that relies heavily on a security governance framework and the availability of resources to mitigate cyber risks. Since every business process is unique, there is no one-size-fits-all framework for cyber governance. A typical framework in any organization includes 

  • Review of potential risks

  • Escalation/de-escalation of risks 

  • Involvement of the Board in mitigating risk decisions 

  • Ensuring that the framework works seamlessly 

  • Structuring cyber security system

  • Code of practices are implemented properly

What are the major components of cyber security governance?

Some of the key components of developing robust cyber security governance include : 

  • Governance -Governance refers to the system by which an organization controls and manages IT security. Understanding how cyber security risks may impact your business goals and objectives establishes the roadmap to determining IT operations. This paves the way to designing a robust governance structure that helps in improving the overall cyber risk management strategy. Once an organization has a clear scope and appropriate resources, individuals or dedicated teams are assigned to take action and make informed decisions. Developing a strategic action plan, policies and establishing key performance indicators (KPIs) fall under governance. 


  • Technology -Since business operations differ depending on the size, location, and scope of the business, so does the technological requirement to sustain business operations and growth.  The organization must ensure basic technological infrastructure that helps protect its assets to withstand cyber threats. To mitigate foreseeable cyber threats and ensure security, organizations may also allocate funds or resources to procure sufficient technological tools. This may include computers, networks, the cloud, and the physical environment for data protection. Depending on the technical aspects of cybersecurity, organizations may conduct routine network penetration tests and security assessments of physical components to deal with cyber risks.


  • Operations - Operations refer to how an organization brings together governance and technology in action. Having a standardized process in place ensures the quality and consistency of the risk management approach. On the contrary, inconsistent and ineffective governance plans will eventually lead to pitfalls and security breaches. In the same manner, outdated technological tools will lead to compromises and cyber-attacks even if a robust governance plan is put in place. Therefore, an organization needs to enforce accountability and consistency in its operational process to meet compliance across all levels. For instance, if an organization possesses great technological tools for cyber risks detection but an inconsistent incident response plan, then it will still be at risk. Implementing risk and vulnerability management and awareness programs will help address existing and future risks within that organization.  

What are security governance principles?


There are six core security governance principles. These include -


  • The first principle is to establish information security governance as per the organization’s structure and objectives. The management should ensure that information security protocols should be well integrated with the latest information technology to establish accountability within the organization. 

  • The second principle dictates adopting a strategic approach based on potential risks. Based on the risk appetite, the resources and budget should be allocated. This also prevents financial losses in the future and reduces liability risks. 

  • As per the third principle, investments should be intended to fulfill a business or organizational objectives. The capital and expenditure should lead to regulatory compliance.  

  • The fourth principle says that there should be conformity in the internal and external requirements. External requirements include legislation, certifications, etc., and internal requirements include risk management approaches based on organizational objectives.

  • According to the fifth principle, fostering a positive environment and fulfilling stakeholders’ expectations is crucial. 

  • From the governance perspective, it is important to review an organization’s security performance concerning business outcomes. Mandate reviews, monitoring, and audits help enhance business performance.

What are the five goals of information security governance?

The information security governance should fulfill five main goals or outcomes enlisted below : 

  • Risk management -One of the main goals of information security governance is risk management. This includes identification, management, reduction, and prevention of potential risks and their ill impact on organizational resources.

  • Resource management -The objective of following a strategic risk management approach is to align with budget and available resources without expending extra. 

  • Policy alignment -Alignment of security policies with organizational objectives helps achieve optimum value. 

  • Performance measurement -To ensure that organizational goals and objectives are met, it is required to compare performance using set metrics.

  • Deliver value - All the investments related to information security governance should be aimed at delivering value while keeping in mind the various needs of stakeholders.

Can I learn cyber governance for free?

Yes, you can learn cyber governance for free by simply enrolling yourself into one or more of the courses offered at Great Learning. These are self-paced and beginner-friendly courses that will equip you with the required skill set to excel in the field of cyber security. 
Subscribe to Academy Pro+ & get exclusive features

$29/month

No credit card required

Learn from 40+ Pro courses

Access 500+ certificates for free

700+ Practice exercises & guided projects

Prep with AI mock interviews & resume builder

FREE
Cyber Forensics
star   4.54 44.2K+ Learners
1 hr
FREE
Network Security
star   4.52 65.9K+ Learners
1 hr
FREE
Introduction to Cyber Crime
star   4.51 13.7K+ Learners
0.5 hr
FREE
Introduction to Ethical Hacking
star   4.5 511.1K+ Learners
2 hrs

Similar courses you might like

FREE
Cyber Security For Leadership
star   4.54 15K+ Learners
1 hr
FREE
Career in Cybersecurity
star   4.4 19.8K+ Learners
1 hr
FREE
Types of Cyber Security
star   4.51 64.7K+ Learners
0.5 hr
FREE
Become an Ethical Hacker
star   4.34 53K+ Learners
1 hr

Related Cyber Security Courses

50% Average salary hike
Explore degree and certificate programs from world-class universities that take your career forward.
Personalized Recommendations
checkmark icon
Placement assistance
checkmark icon
Personalized mentorship
checkmark icon
Detailed curriculum
checkmark icon
Learn from world-class faculties
Enroll For Free